


Cloud accounting security best practices for remote teams start from one fact: your general ledger, payroll files and client tax data now sit behind a login page that anyone on the internet can reach. In an office, a firewall and a locked door did part of the work. With staff on home Wi-Fi, personal laptops and offshore time zones, the login, the device and the person holding it are the whole perimeter.
For CPA firms and tax preparers, these controls are also a legal requirement. The FTC treats tax preparation firms as financial institutions under the Gramm-Leach-Bliley Act, and in August 2026 the IRS and its Security Summit partners again reminded practitioners that federal law requires a Written Information Security Plan.
The cloud platform itself (QuickBooks Online, Xero, Sage Intacct, NetSuite) is rarely the weak point. Breaches at accounting firms usually start with a person: a phished password, a reused credential from another site, a laptop left logged in, or an ex-employee whose access was never removed.
Remote work multiplies those openings in specific ways:
Most of the fixes are well understood and inexpensive.
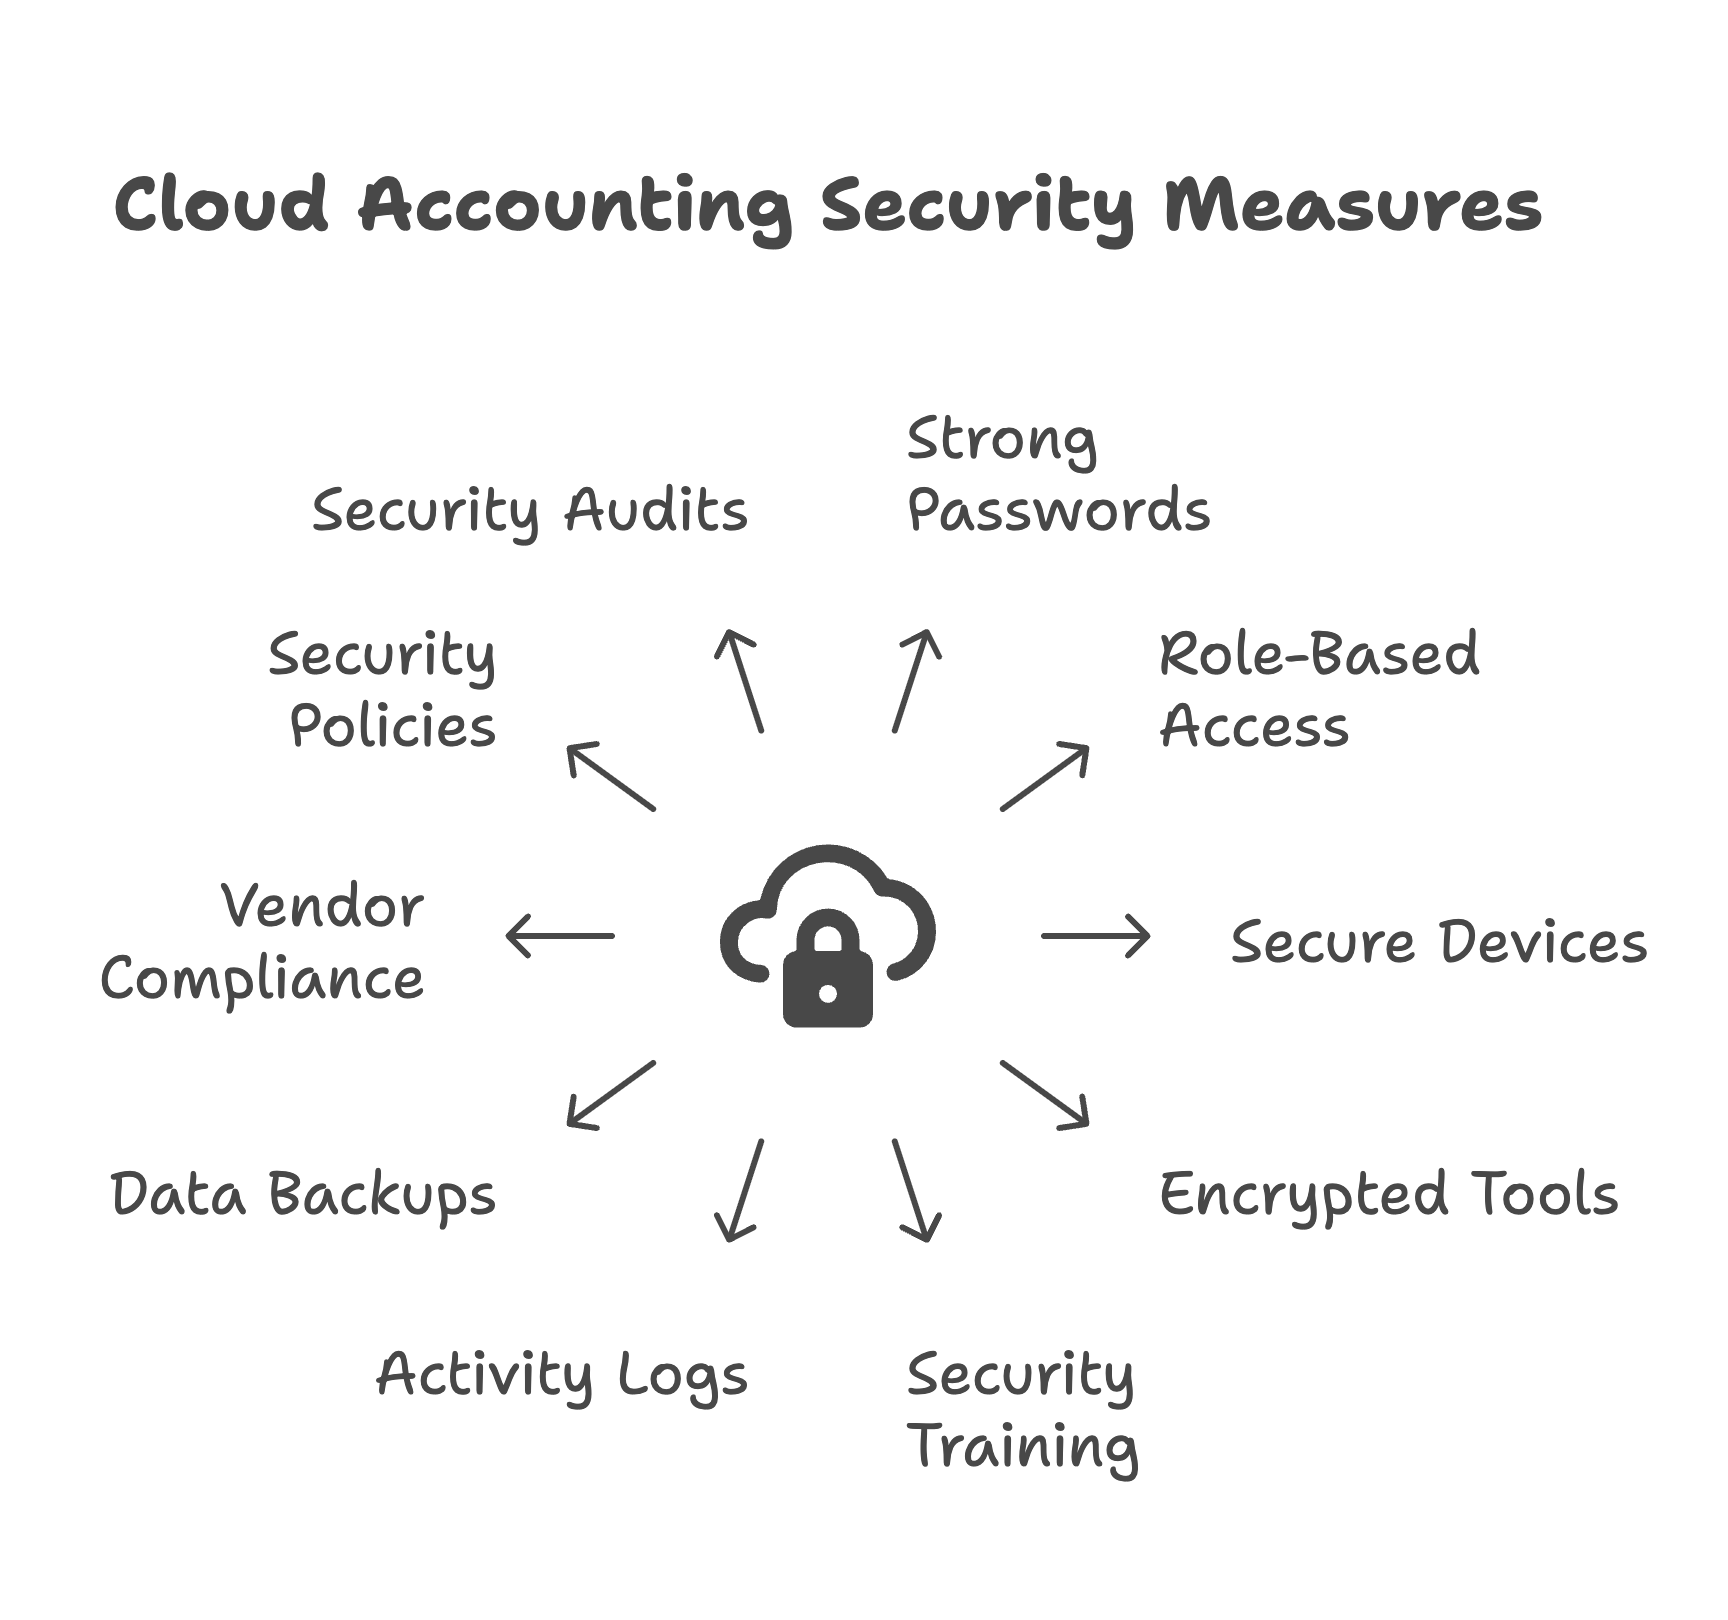
If your firm prepares returns or handles client financial data, the FTC Safeguards Rule (16 CFR Part 314) applies. Its main requirements map directly onto a remote setup.
| Requirement | What the rule says | How it looks for a remote team |
|---|---|---|
| Qualified Individual | One named person oversees the security program | A partner or IT lead owns the WISP; if outsourced, a senior employee supervises the provider |
| Multi-factor authentication | Required for anyone accessing customer information | MFA on the accounting platform, email, tax software, document portal and VPN |
| Encryption | Customer data encrypted at rest and in transit | Full-disk encryption on every laptop; encrypted portals, no email attachments |
| Access monitoring | Log and monitor authorized users' activity | Platform audit logs reviewed monthly; alerts for new-country logins |
| Testing | Annual penetration test and vulnerability scans every six months, unless you monitor continuously | Scheduled scans of firm-managed devices and any servers |
| Secure disposal | Dispose of customer data within two years of last use, with exceptions | Retention schedule for client folders, including copies on staff devices |
| Breach notice | Notify the FTC within 30 days if 500+ consumers' unencrypted data is acquired | Incident plan names who files and who calls the IRS |
| Board report | Qualified Individual reports in writing at least annually | Annual memo to the partners or owner |
Firms that hold information on fewer than 5,000 consumers are exempt from some of these provisions, such as the written risk assessment and the annual report. MFA, encryption and the core program still apply. The IRS's Publication 4557, Safeguarding Taxpayer Data translates these rules into checklists for small practices. For a deeper look at how AICPA, IRS and FTC rules overlap when work moves offshore, see our guide to data security compliance for CPA firms.
MFA is the single control that stops most credential attacks. Turn it on for every system that touches client data, not only the general ledger. Email matters most, because a compromised mailbox is how attackers reset passwords everywhere else.
Prefer an authenticator app or a hardware security key over SMS codes, which can be intercepted through SIM swapping. Disable "remember this device" on shared or personal computers.
Current federal guidance has moved away from forced 90-day password changes and complex character rules. NIST SP 800-63B-4, finalized in 2025, favors long passphrases (15 characters or more when a password is the only factor), screening against lists of breached passwords, and changing a password only when there is evidence of compromise.
In practice: issue a business password manager to every staff member, require unique passphrases for each system, and share client credentials only through the manager's vault, never in a spreadsheet or chat message.
Least privilege means each person sees only what their job needs. A bookkeeper reconciling bank feeds doesn't need payroll admin rights, and a seasonal tax preparer doesn't need access to last year's client folders.
Concrete steps:
Segregation of duties still matters when the team is remote. The person who adds a vendor should not be the person who approves the payment. Our article on internal controls testing for small businesses shows how to test that these splits actually work.
A cloud platform can be well protected and still be exposed by an infected laptop. Firm-issued, centrally managed devices are the cleanest answer. If staff use personal machines, set minimum standards and verify them.
Mobile device management lets you wipe firm data from a lost phone or laptop remotely, which turns a potential breach into an inconvenience.
Email attachments are the leakiest part of most firms' workflow. Use a client portal or a business-tier file sharing service with encryption, link expiry and download logs. Turn off personal sync of client folders to home computers where you can.
Going paperless helps here, because a single document system is easier to lock down than paper, scanners and local drives combined. Our paperless accounting implementation guide covers the setup steps, and the comparison of cloud practice management software lists the security features worth checking.
Business email compromise works well against remote teams, because staff are used to receiving instructions in writing. Set a firm rule: any change to vendor bank details, payroll direct deposit or wire instructions is confirmed by calling a number already on file, never one in the email.
For the wider set of controls that catch payment fraud, see fraud prevention 101.
Most cloud accounting platforms record logins, IP addresses and changes to transactions. The Safeguards Rule requires you to monitor that activity. A practical routine for a small firm:
If you connect apps through APIs (bank feeds, expense tools, payroll), include those integration accounts in the review. Each connection is a credential that can be abused. Our guide to API integration for accounting workflows explains how to scope those permissions tightly.
Your cloud provider protects against its own hardware failures. It doesn't protect you against a staff member deleting a year of transactions or ransomware encrypting a synced folder. Use a third-party backup for the accounting file and document storage, keep at least one copy that is not continuously synced, and test a restore every quarter. Write down how long you could operate without the system, then check that the backup schedule matches.
Any vendor or outsourcing partner that touches client data inherits your obligations. Ask for a current SOC 2 Type II report or ISO 27001 certificate, read the exceptions section, and confirm the report covers the services you actually use. When offshore staff work in your systems, the best practices for managing an offshore accounting team apply alongside these security terms. Contracts should cover data location, breach notice timing, subcontractors and return or deletion of data at exit. Our checklist on SOC 2 and ISO 27001 vendor due diligence lists the questions to ask, and data security controls for offshore bookkeeping covers DLP and access reviews for offshore staff.
The WISP is where all of the above becomes policy. The IRS template in Publication 5708 gives small firms a starting outline. Keep it short enough that staff will read it, and update it whenever you add a system or change how people work.
Training should be short and frequent: a 20-minute session at onboarding, quarterly refreshers, and simulated phishing emails with follow-up for anyone who clicks.
Then rehearse. Walk the team through a scenario, such as a preparer's laptop stolen from a car, and check that everyone knows who to call. The IRS data theft guidance for tax professionals says to contact your IRS Stakeholder Liaison immediately, along with state tax agencies and law enforcement. Our data breach response guide for tax professionals covers the reporting sequence in detail.
A firm with three partners, four staff across three states and one offshore bookkeeper might roll this out over a quarter.
Most of the cost is staff time. The tools involved are commonly bundled in business email and productivity plans the firm may already pay for. For how distributed firms structure the rest of their operations, see our remote-first CPA firm operations guide.
Major platforms encrypt data and undergo independent audits, so the platform is usually the strongest link. Risk comes from how users sign in and where they download data. With MFA, role-based access and managed devices, cloud is generally safer than files on an office server.
Yes. The IRS states that tax and accounting professionals are legally required to have one under federal law, regardless of size. Firms with fewer than 5,000 consumer records are exempt from some Safeguards Rule provisions, but the written plan itself is still expected.
These platforms already use encrypted HTTPS connections, so a VPN isn't strictly needed for the login itself. A VPN or secure access service still helps on public Wi-Fi and when staff connect to firm file servers or remote desktops.
Quarterly is a reasonable baseline for most firms, plus an immediate review whenever someone leaves or changes roles. Firms with seasonal staff should add a review right after tax season ends.
Remotely lock or wipe it through MDM, reset the user's passwords and revoke active sessions, then check the audit logs for unusual access. If taxpayer data may have been exposed, contact your IRS Stakeholder Liaison and follow your WISP's notice steps.
Madras Accountancy supports US CPA firms with offshore accounting and tax staff who work inside your systems under MFA, role-based access and monitored, firm-controlled environments. If you want added capacity without loosening your security standards, contact our team to discuss how we set up access for your firm.

Section 4960's 21% excise tax now reaches far more nonprofit employees. See who is a covered employee in 2026 and what changed.

The Section 45S paid family leave credit is permanent for 2026 with new options. See who qualifies, the amounts, and how to claim it.

Opportunity zones become permanent in 2027 under the One Big Beautiful Bill. See the new deferral, rural bonus, and the 2026 handoff.



